 PandaShield
PandaShield performs deterministic SAST, dependency vulnerability scanning, and secret detection inside isolated gVisor sandboxes. Actionable findings, cryptographic PDF reports, and zero unverified fixes.
Every check is deterministic, isolated, and backed by verifiable evidence.
Scans code for SQL injection, SSRF, broken access control, and OWASP Top 10 vulnerabilities with exact file, line, and code snippets.
Direct integration with OSV advisory databases. Maps lockfiles to known CVEs without executing untrusted package install hooks.
Pattern-matching and entropy-based identification of exposed API keys, private certificates, and authentication tokens.
Every customer repository is analyzed inside a hardware-isolated runsc sandbox with dropped capabilities and zero network egress.
Generate C-level executive summaries and detailed technical reports with cryptographic watermarks, report hashes, and page numbers.
Proposes minimal, audited patches from redacted code context. No code changes are ever applied automatically without your explicit approval.
Built specifically to analyze untrusted third-party code without host compromise.
Analysis containers run with --network none. Untrusted code cannot exfiltrate environment variables, data, or credentials.
Analysis executes in an internal Docker-in-Docker daemon reachable only over mutual TLS (mTLS) by background worker containers.
Workspace data is isolated in PostgreSQL queries and verified across every API route with strict 404 cross-tenant rejection.
The backend origin rejects all traffic that bypasses Cloudflare Pages, maintaining same-origin HttpOnly session cookies.
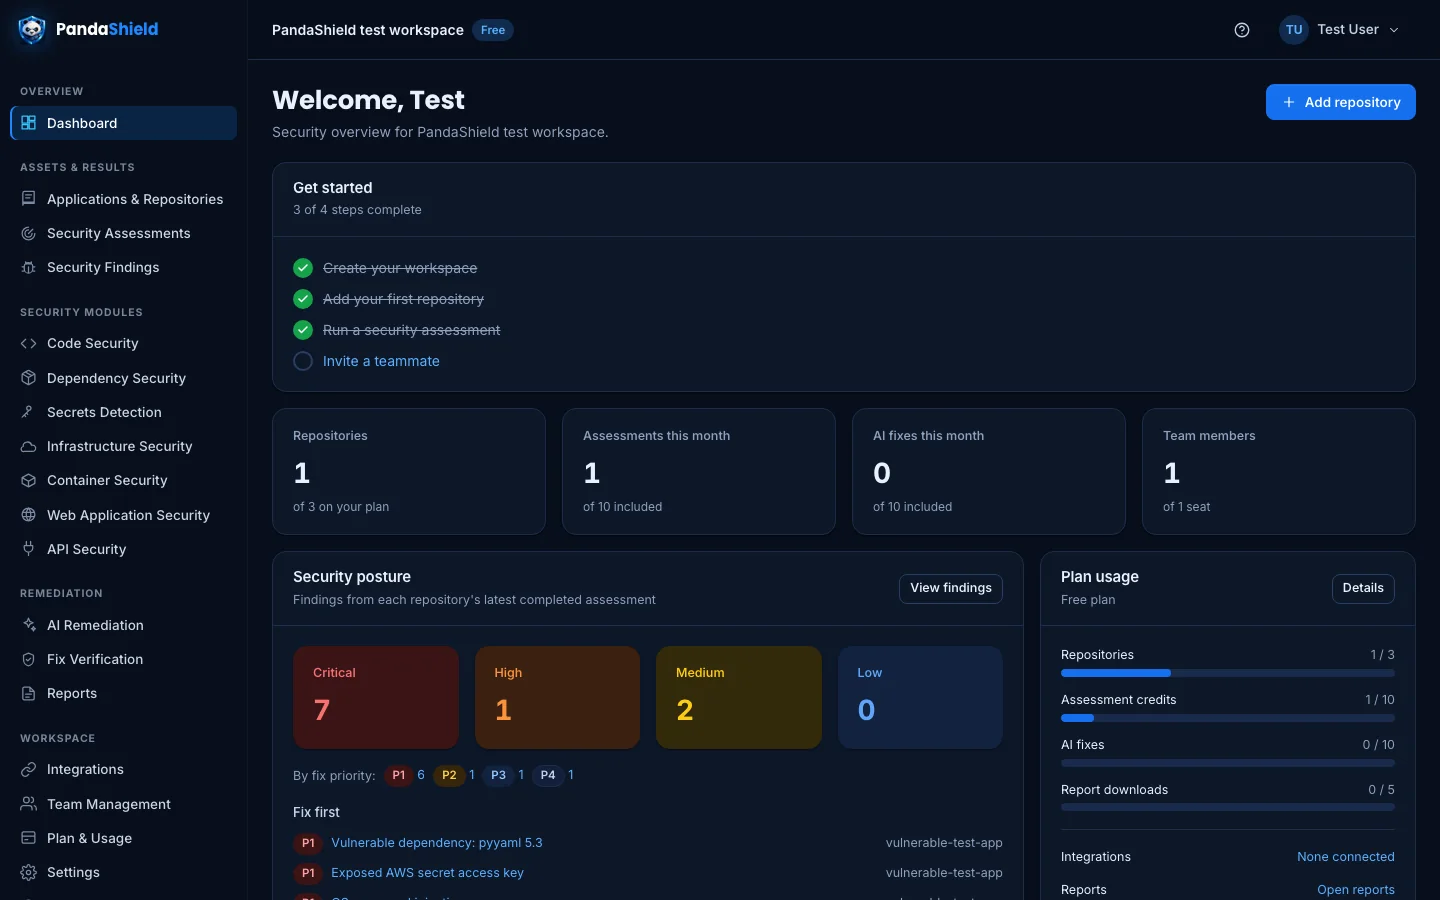
Real screenshots captured from PandaShield evaluating its test suites.
We are onboarding an initial group of 5–10 development teams before opening to 15 testers.
To ensure high-touch onboarding and cluster stability, our initial staging cohort is limited to 5–10 development teams.
To request an invite code and workspace onboarding link, click below to email the deployment team directly with your organization details.
Request Pilot Invitation via Email →krishnamadhu162308@gmail.com • No credit card required.
Uploaded source code is decrypted temporarily in memory and deleted immediately after assessment completion. Secrets are masked before storage.
The staging environment is intended for test evaluations. Assessments are non-destructive and do not perform active network penetration.
Have questions or feedback? Contact the engineering team at support@pandashield.internal or reach your deployment lead.